
Hackers claimed to have hacked the ATB website and stolen data, the company denies the leak
The ATB retail chain confirmed an attempted hacker attack on its online resources after a page appeared on the online store's website on October 5 demanding payment of $400,000 in cryptocurrency. At the same time, the company states that there was no leak of customers' personal data.
This was reported by dev.ua to Serhiy Demchenko, head of corporate communications of the ATB network.
"Yes, there was indeed an attempted hacker attack on the company's resources. Fortunately, there was no data leak - customers' personal data was not stored on our resources at all. We are currently restoring operations, and all resources will be fully operational soon", - he stated.
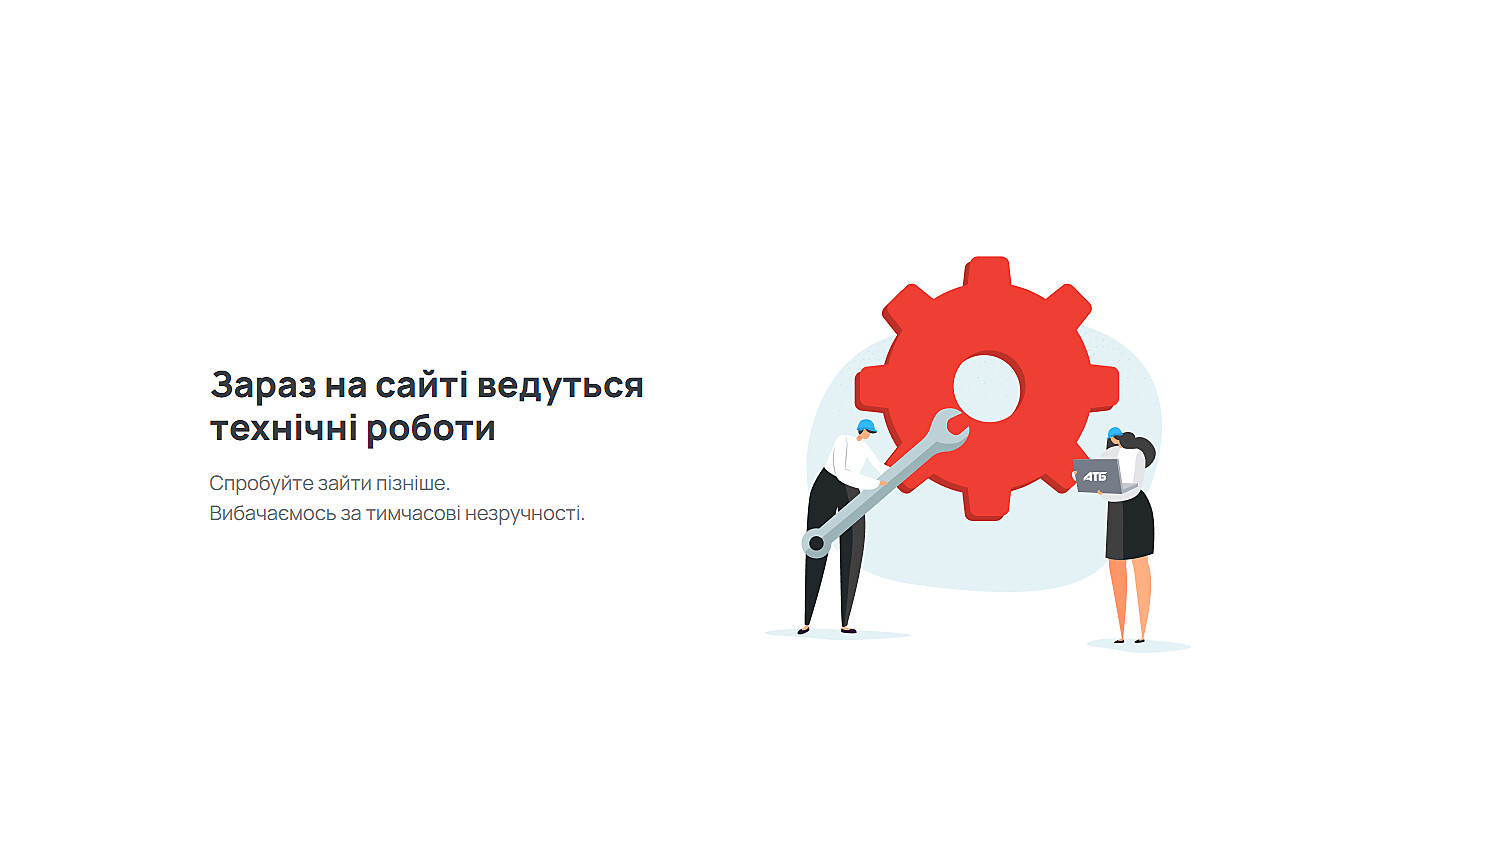
At the time of writing, the site atbmarket.com no longer displays the page with the attackers' demands. Instead of the catalog, users see a message about maintenance work asking them to come back later.
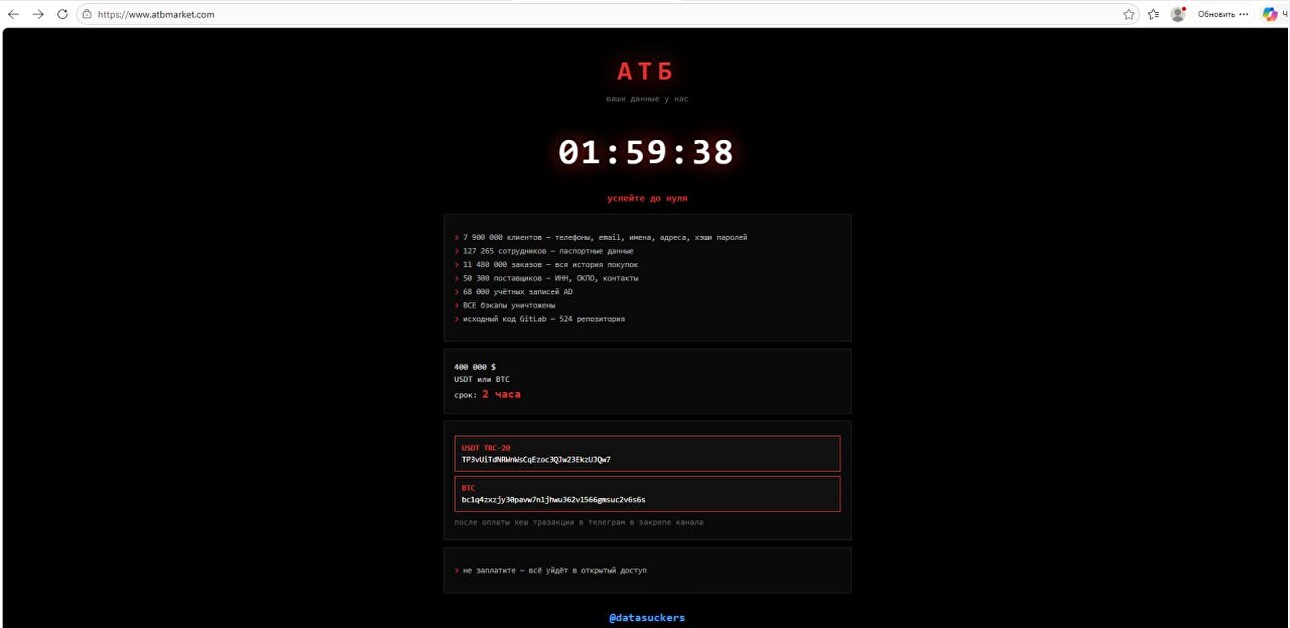
Earlier, a page appeared on the ATB domain with the inscription "ATB - your data is with us", a countdown timer, and a demand to transfer $400,000 in USDT or Bitcoin within two hours. If refused, the authors of the message threatened to publish the allegedly obtained information.
The attackers claimed to have data of 7.9 million customers, including phone numbers, email addresses, names, addresses, and password hashes. They also claimed to have obtained passport data of over 127,000 employees, the history of 11.48 million orders, and information about over 50,000 suppliers.
In addition, the message mentioned access to 68,000 Active Directory accounts, source code of 524 GitLab repositories, and alleged destruction of backup copies.
ATB does not confirm these claims. On the contrary, the company directly denied the leak of customer data and noted that customers' personal information was not stored on the attacked resources.
Thus, the only confirmed fact currently is the attempted cyberattack and the appearance of an unauthorized message on the ATB resource. The scale of access to internal systems, employee and supplier data, and source code claimed by the attackers has not been independently confirmed.
dev.ua notes that the ransom demand text was indexed directly on the pages of the network's official website. This could indicate defacement - unauthorized replacement of web page content - or compromise of a separate part of the web infrastructure.
Currently, ATB continues to restore its online resources. The company has not yet specified when the online store will return to full operation.
